A software engineer’s earnest effort to steer his new DJI robot vacuum with a video game controller inadvertently granted him a sneak peak into thousands of people’s homes.
While building his own remote-control app, Sammy Azdoufal reportedly used an AI coding assistant to help reverse-engineer how the robot communicated with DJI’s remote cloud servers. But he soon discovered that the same credentials that allowed him to see and control his own device also provided access to live camera feeds, microphone audio, maps, and status data from nearly 7,000 other vacuums across 24 countries. The backend security bug effectively exposed an army of internet-connected robots that, in the wrong hands, could have turned into surveillance tools, all without their owners ever knowing.
In late 2025 and early 2026, a series of independent disclosures by software maintainers, security researchers, and national cyber authorities converged on an unsettling conclusion: for months, the update mechanism of one of the world’s most widely used open-source text editors had been quietly subverted. What initially appeared to be an isolated infrastructure anomaly was ultimately revealed to be a sustained compromise of the Notepad++ update pipeline, stretching back roughly six months. As investigators reconstructed the timeline, tracking unauthorized access to hosting infrastructure, lingering credentials that outlived initial remediation, and selectively altered update responses, a far more deliberate operation came into focus. This report is the product of analysis and parallel reconstruction of all public reporting on Lotus Blossom with additional research by DTI, drawing together technical forensics, victimology, and strategic context to assess both the campaign and the actor behind it.
The maintainer of popular open-source data transfer tool cURL has ended the project’s bug bounty program after maintainers struggled to assess a flood of AI-generated contributions.
Curler-in-chief Daniel Stenberg last week lodged a GitHub commit named “BUG-BOUNTY.md: we stop the bug-bounty end of Jan 2026”.
Most of the above advice comes via CISA, America’s cyber defense agency, but the latest is from CERT-FR, France’s equivalent, in conjunction with the U.K.’s agency. There is already plenty of Wi-Fi advice, but to completely disable the interface is new.
A new malware campaign targeting Brazilian users has emerged, using WhatsApp as its primary distribution channel to spread banking trojans and harvest sensitive information.
This sophisticated attack leverages social engineering by exploiting the trust victims place in their existing contacts, making the malicious files appear legitimate.
The campaign begins with phishing emails containing archived VBS scripts that employ advanced obfuscation techniques to evade detection by security software.
A critical security flaw in WhatsApp has allowed researchers to expose the phone numbers of 3.5 billion users, marking one of the most significant data leaks ever documented.
This vulnerability, rooted in the app’s contact discovery feature, persisted despite warnings to Meta dating back to 2017, raising serious concerns about user privacy on the world’s most popular messaging platform.
The exploit relies on WhatsApp’s built-in mechanism for finding contacts, which reveals whether a user is on the service and public details like profile pictures and status texts when a phone number is entered.
Security researchers from the University of Vienna demonstrated the flaw by systematically querying billions of potential numbers, confirming active accounts at a rate of over 100 million per hour without any restrictions from WhatsApp.
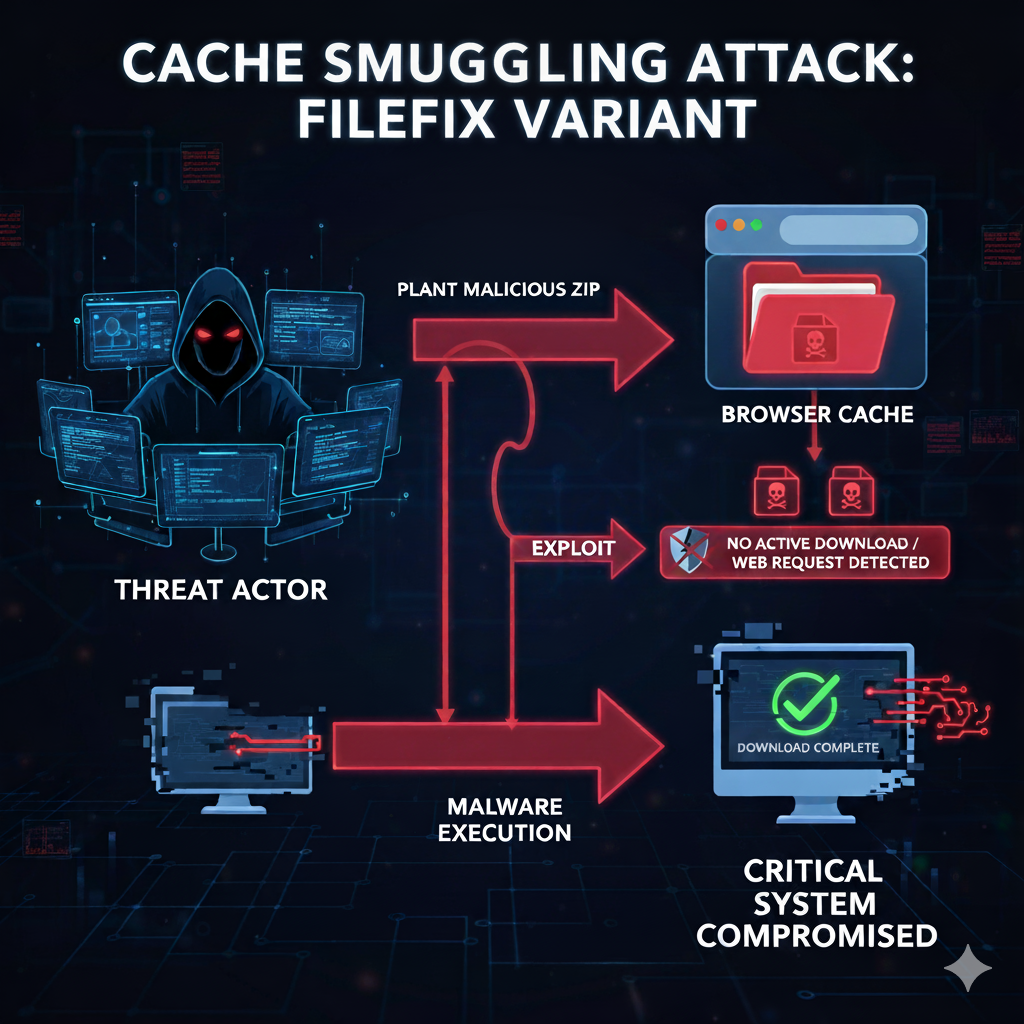
BLUF: Threat actors are using a sophisticated variant of the FileFix social engineering attack, known as cache smuggling. It plants malicious ZIP archives in a victim’s browser cache. This enables execution of malware while bypassing security software checks for active file downloads or web requests.
The new FileFix campaign lures victims with a spoofed tool such as “Fortinet VPN Compliance Checker.” The user is told to copy a seemingly innocuous network file path and paste it into the Windows File Explorer address bar.
However, the text copied to the clipboard is heavily padded with spaces, concealing a malicious PowerShell command that is executed in headless mode when the user presses Enter.
The principle behind the attack is ‘cache smuggling’. When the user accesses the phishing page for the first time, JavaScript requests the browser to fetch a payload which has been disguised as a legitimate JPEG image. The browser caches this file, which actually contains a malicious ZIP archive.
The PowerShell script scans the local browser cache, extracts the hidden archive, and launches the malware from the local system without initiating any new web requests.
This method circumvents established security programmes that monitor network traffic or file downloads. The technique is being rapidly adopted by various threat actors, including ransomware gangs.
Action points
It is critically important to never copy and paste text or commands provided by an external website into operating system dialogue boxes, terminal windows, or address bars.
Organisationally, Endpoint Detection and Response (EDR) capabilities should be used that look for PowerShell scripts interacting with or manipulating browser cache files, or which execute in a hidden (headless) manner. These are clear indicators of this attack vector.
Browsers and security software should restrict or audit the automatic execution of files retrieved from the browser cache by command-line utilities.
Consider implementing’zero trust’ security policies that limit the execution of unrecognised executable files, even if they originate from what appears to be a local path, such as the extracted file from the cache.